Drive Productivity, Backed by Real-World Security Delivery

Azure Solution Architect
Azure Administrator Associate
Azure Network Engineer Associate
Microsoft Certified: DevOps Engineer Expert
Azure Security Engineer Associate
Administering Windows Server Hybrid Core Infrastructure
Azure Virtual Desktop Specialty
Microsoft Security Operations Analyst Associate
Administering Information Security in M 365

What Happens When Azure Security Is Not Prioritized?

What Happens When Azure Security Is Not Prioritized
  • Misconfigurations stay hidden:

    One open storage account or loose network rule can expose data before anyone notices.

  • Access keeps growing:

    Without governance, too many people and workloads hold permissions they don't need.

  • Threats blend into the noise:

    Your team can't tell a real attack from a false alarm, so response gets slow.

  • Audits turn into scrambles:

    You spend weeks pulling evidence together instead of producing it on demand.

  • Security falls behind the cloud:

    Every new workload or migration widens the gap between what you run and what you protect.

Where We Help Across Your Azure Security Journey?

Our Services

We review your current configuration, where the gaps are, and how exposed you are. We evaluate your Azure environment against best security practices and industry compliance standards.

Our team uses Microsoft Entra ID, Conditional Access, PIM, and RBAC to lock identity. Tighten access governance so every user and workload operates on least privilege, without losing visibility into who can do what.

We use Microsoft Defender to flag risk across your workloads and keep your security posture moving in the right direction, not just snapshot it once and walk away.

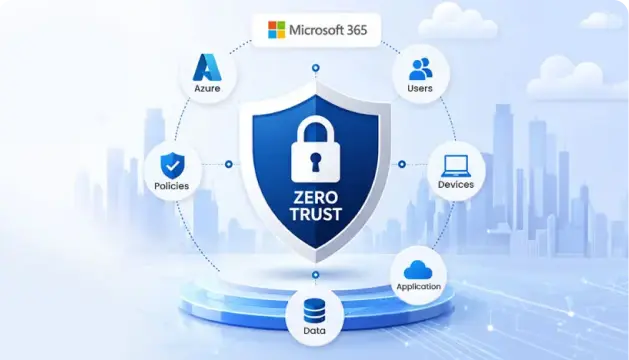
Our team builds zero trust security using Entra ID, Conditional Access, and Defender for Cloud, so your Azure footprint has fewer places for an attacker to hide.

Our Azure experts design network architecture with NSGs, Azure Firewall, and Private Link so traffic is controlled, exposure is minimized, and lateral movement gets shut down early.

Data at rest, data in transit, keys, secrets, certificates, all of it needs a home and a policy. Azure Key Vault and layered encryption controls provide that, with tighter oversight of how sensitive data moves through your environment.

Servers, containers, storage; each one has a different threat profile, and we treat them that way. Microsoft Defender for Servers, Containers, and Storage lets us apply controls that fit the workload instead of a one-size-fits-all policy.

We map your environment to the Azure Security Benchmark and CIS frameworks, then turn that into enforceable policy, documented controls, and evidence you can produce when asked.

Microsoft Sentinel and Defender XDR bring your security signals into one place, cut through the alert noise, and give your team a real shot at responding before damage is done.

We use Azure Policy and Defender for Cloud to set secure baselines, catch deviations as they happen, and keep your environment enforced against the standard, not just compliant on day one

Where We Help Across Your Azure Security Journey?

Our Approach for Azure Security Services?

1

Assessment and Strategy

We evaluate your existing Azure environment, check the highest-risk gaps, and build a plan shaped by your actual environment and compliance needs, not a generic checklist.

2

Architecture and Design

Our experts design identity, network, and data protections aligned to Zero Trust principles and Microsoft's Well-Architected Framework.

3

Implementation

We deploy the controls, Entra ID policies, Defender, Sentinel, Key Vault, and Azure Firewall, with minimal disruption to running workloads.

4

Monitoring and Response

Once live, we monitor continuously, tune detection rules, and respond to incidents as part of a standing security operation.

5

Ongoing Optimization

We revisit your posture regularly as Azure's security capabilities and your environment both evolve.

Azure Security Use Cases

01

Alert Fatigue

CHALLENGE

Security tools exist, but alerts pile up faster than the team can review them.

HOW WE HELP

We deploy Microsoft Defender for Cloud and Sentinel with tuned detection rules and managed monitoring.

RESULT

Real threats surface first, with fewer false positives consuming your team's time.

02

Over-Permissioned Identities

CHALLENGE

Access sprawled across the organization with no clear record of who can reach what.

HOW WE HELP

We implement Microsoft Entra ID governance, Conditional Access, and PIM to enforce least-privilege access.

RESULT

A reduced attack surface and auditable, deliberate access control.

03

Compliance Audit Approaching

CHALLENGE

An audit is coming up and nobody's confident the current Azure setup will pass.

HOW WE HELP

We run a full compliance gap assessment against the relevant framework, then remediate before the audit date.

RESULT

An audit-ready environment with documented, defensible controls.

04

Migration Introduced New Exposure

CHALLENGE

Workloads moved to Azure faster than security kept pace, leaving configuration gaps behind.

HOW WE HELP

We run a post-migration security review across identity, network, and data layers, and close what's exposed.

RESULT

A hardened environment that matches the security standard the migration was supposed to deliver.

05

No Internal Bandwidth for Security Operations

CHALLENGE

Controls are in place, but nobody has the time to monitor them continuously.

HOW WE HELP

We provide managed security monitoring, incident response, and posture reviews as a standing service.

RESULT

24×7 coverage and continuous improvement instead of a security setup that quietly ages out of date.

06

Sensitive Data With No Clear Protection

CHALLENGE

Customer and business data sits across Azure storage, databases, and apps, but nobody can say what's sensitive, where it lives, or who can reach it.

HOW WE HELP

We discover and classify your data, then apply Microsoft Purview policies, encryption, and Azure Key Vault controls to protect it.

RESULT

Sensitive data is visible, protected, and locked down to the people who need it.

Why Choose Beyond Key for Azure Security Services?

Trusted Microsoft Solutions Partner

We are a Microsoft Solutions Partner with certified professionals experienced in Zero Trust architecture, identity governance, and Azure-native security tooling.

21+ Years of Technology Experience

We've delivered Microsoft-centric security work for enterprises across 30+ geographies, backed by our own SOC 2 Type II and ISO certifications.

Industry-Focused Security

Our Azure security experts have hardened environments for healthcare, finance, technology, and manufacturing clients, each with different compliance obligations and risk profiles.

Our Real-World Azure Success Stories

Modernized legacy workloads and enhanced security with Azure-native networking, governance, and application services.

Explore more →

Reduced cyber risk and strengthened compliance using Azure Firewall, Defender, Policy, and DDoS Protection.

Explore more →

Improved application performance and scalability while optimizing infrastructure costs through cloud transformation

Explore more →

Ready to Strengthen the Security of Your Azure Environment?

You don't need to know exactly which control is missing before talking to us. Tell us the concern, an upcoming audit, alert fatigue, an identity gap, or a post-migration review, and we'll help you find the right starting point.

Frequently Asked Questions

Azure Security Services are the tools, configurations, and practices used to protect identities, data, networks, and workloads running in Microsoft Azure, covering identity and access management, network security, data protection, and continuous threat detection.

They close the gaps native settings leave open by enforcing least-privilege access, segmenting networks with Zero Trust principles, encrypting data at rest and in transit, and continuously monitoring for unusual activity through Microsoft Defender for Cloud and Sentinel.

An Azure security consultant assesses your environment for misconfigurations and gaps, designs and implements identity, network, and data protections, and sets up ongoing monitoring so new risks get caught as your environment changes.

Azure Security Services costs depend on the scope and size of your environment. They also use different pricing models. From monthly subscriptions to fixed-fee engagement model, you can choose the model that fits your budget and business needs.

Yes. It can be aligned with compliance standards such as SOC 2, GDPR, HIPAA, and ISO 27001 so that it's easy for auditors to have a look at documentation and evidence.

Yes. We run a full assessment covering identity configuration, network security, data protection, and Microsoft Secure Score, and deliver a prioritized remediation plan.

Yes. At Beyond Key, we provide ongoing monitoring services by using Defender for Cloud and Sentinel. It ensures that the data is checked for threats to avoid mishaps.