Microsoft 365 Security & Compliance Case Study | Beyond Key
Read how a renowned financial leader strengthened their Microsoft 365 security and compliance posture with Beyond Key.
Explore in detail →


Safeguard your organization with Beyond Key's red team penetration testing services, combining offensive security expertise and real adversary tradecraft to expose gaps that scans and checklist audits miss.
Red team penetration testing simulates real-world cyberattacks to evaluate your organization’s security defenses. Ethical hackers use techniques such as social engineering, network intrusion, and application exploitation to identify vulnerabilities, test defensive capabilities, and assess how effectively your team detects and responds to threats.
You've run the audits and patched what the tools flagged. But attackers don't follow your checklist. Here's what we hear most often
We pass our audits, but would we survive a real attack Compliance shows you met a standard. It doesn't show how far someone could get once they're inside.
We can't tell if our credentials are secure Weak, reused, or exposed passwords often sit unnoticed until someone uses them.
Our SOC has never faced a patient attacker Alerts are easy to tune against known tests. A quiet, goal-driven adversary is a different story.
Our people are the soft spot One convincing phishing email can undo a lot of good tooling.
One foothold could become full control Small gaps in Active Directory or Entra ID can chain together into a domain-level breach. Red team security testing answers these questions with evidence, not assumptions.
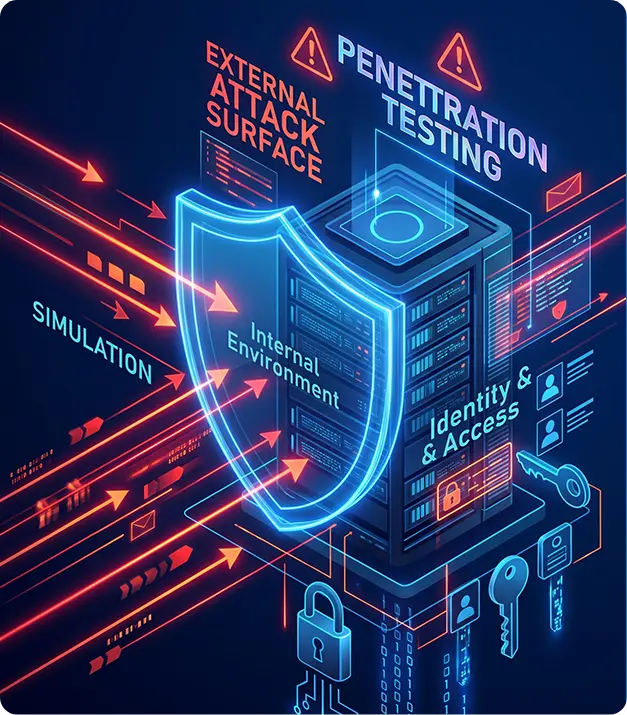
We simulate real attacks across your external systems, identities, people, and internal environment. The goal is to find the attack paths that standard security testing misses.
Internet-Facing Systems : We look for weak spots in the servers and systems anyone can reach from the internet.
Web Applications: We test your web apps for flaws that could lead to unauthorized access, data exposure, or a full compromise.
APIs: Our team checks authentication, authorization, and business logic so your APIs don't hand over sensitive functions or data.
Remote Access: We test VPNs, remote desktops, and other remote tools for gaps an attacker could use.
Cloud Services: We review exposed cloud resources and configurations that could give an attacker a way in.
Active Directory: We find misconfigurations, excess privileges, and attack paths that could lead to domain-level compromise.
Entra ID: Our experts review cloud identity settings, permissions, and sign-in controls for weaknesses.
Privileged Accounts: We test whether admin credentials can be stolen or abused to gain higher access.
Authentication Controls: We check your sign-in methods for flaws that could allow credential theft or unauthorized entry.
Identity-Based Attack Paths: We map how one compromised identity could lead an attacker toward your most sensitive systems.
Phishing Simulations: We run safe, targeted phishing tests to see who clicks and where your controls fall short.
Social Engineering: We test how well your people and processes hold up against the tricks attackers really use.
Credential Exposure: Our team looks for leaked or compromised credentials that could be used to get in.
Security Awareness Gaps: We highlight human-layer weaknesses that could increase the risk of successful cyberattacks.
Lateral Movement: We check whether an attacker with a first foothold could move from system to system.
Privilege Escalation: We find routes that take an attacker from limited access to high-level control.
Endpoint Security: We test your endpoint defenses against real attacker techniques and look for ways around them.
Network Segmentation: We check whether your network boundaries actually stop unauthorized movement between critical environments.
Data Access: We test whether an attacker could reach sensitive data, and how well your controls protect it.
Our team uncovers vulnerabilities in AI models and autonomous agents through adversarial testing.
Large Language Models (LLMs)
AI Agents & Bots
AI Applications
Weak credentials opened the door to unauthorized SSH access. Sensitive logins crossed the network in plaintext. Beyond Key ran a red teaming exercise to show how far an attacker could go, then gave the team a clear plan to close the gaps and tighten identity controls.
Every engagement follows a structured, MITRE ATT&CK-aligned process. That keeps results consistent, defensible, and easy to act on.
We agree on goals, boundaries, and the trusted contacts who will manage the exercise inside your company.
We collect open-source intelligence on your organization, your people, and your external footprint.
We try to get in through phishing, exposed services, or application weaknesses.
We move through your environment toward higher-value systems and credentials.
We work toward the agreed goal, such as reaching sensitive data or taking over the domain.
We measure if, how, and how fast your security team spotted and contained the activity.
You get a clear attack narrative, the evidence behind it, and prioritized steps to fix what we found.

We are backed by team members with certified offensive skills and hands-on work in complex enterprise environments.

Our experience in M365, Azure, and Active Directory empowers us to test your Microsoft environment deeply

We know how real Microsoft environments are set up, connected, and secured. We do more than run generic tools.
Read how a renowned financial leader strengthened their Microsoft 365 security and compliance posture with Beyond Key.
Explore in detail →
See how a Middle East manufacturer enhanced its manufacturing security with expert Microsoft 365 support from Beyond Key.
Explore in detail →A Red Team test simulates a real cyberattack to see how well an organization can prevent, detect, and respond to attacks.
Regular penetration testing mainly finds vulnerabilities. Red Team testing goes further by simulating realistic attacks and testing the organization’s overall defenses, including people and processes.
It takes typically a few weeks to a few months, depending on the scope and objectives.
It can test networks, applications, cloud systems, employees, physical security, access controls, and security monitoring/response.
Looking for Digital Transformation?
INDIANA:

16th Floor - South Tower
Indianapolis, IN 46204
United States
ILLINOIS:
Superior St, 707
Chicago, Illinois 60654
United States
Email us for Business
Call Us
AUSTRALIA:
10 Darcy Street
Parramatta, NSW 2150
Email us for Business:
Call Us
Indore Office:
901 A, PU4, Scheme No. 54, Vijay Nagar,
Indore,
Madhya Pradesh 452010,
India
Pune Office:
Awfis, 9th Floor, Off Viman Nagar Road,
Viman Nagar,
Pune, Maharashtra 411014,
India
Hyderabad Office:
F958+CJ4 Lorven Tiara, 4th Floor,
Junction, Kondapur, Laxmi Cyber City,
Whitefields, HITEC City, Kothaguda,
Hyderabad Telangana - 500084, India
Email us for Career:
Email us for Business:
Call Us