AWS security testing
We deploy AWS-certified experts to conduct thorough assessments of IAM, S3, EC2, Lambda, VPC, and all AWS native services.


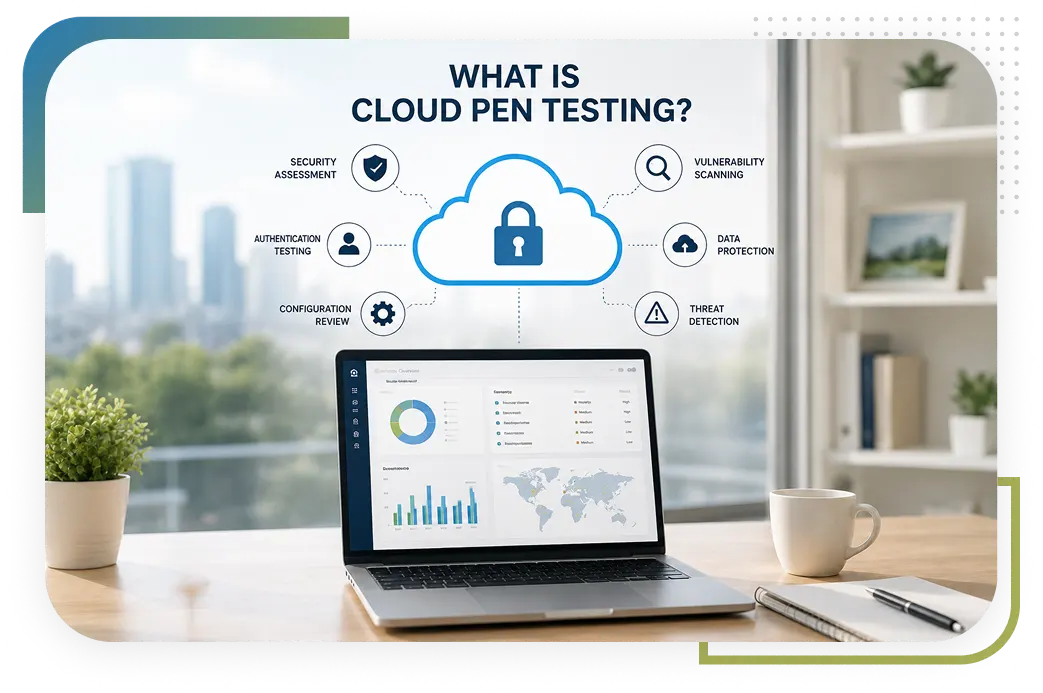
Cloud Pen Testing considers unique architecture and security plateform-expertises of the cloud environment and focuses on simulating authorized cyberattacks on cloud-based platforms (Google Cloud, AWS, or Microsoft Azure). The objective of cloud pentesting services (GCP) is to:

We check abuse of roles, trust policies, token assumptions, and no permission-based access to sensitive data.

Testers evaluate data exposure vulnerabilities. Ensures data encryption, checks snapshot leakage, backup access & more.

Our testers assess cloud workloads & operating system, VM instances, container breakout risks, and Kubernetes control faults.

Pipeline injection, secrets exposure, and build system compromise testing. Our cloud professionals frequently check CI/CD updates.

Application Programming Interfaces (APIs) and cloud apps are highly vulnerable to cyber frauds. We identify insecure API keys & OWASP Top 10.
Network Administrator/ Senior Tech Support Beyond Key
We recommend choosing cloud pentesting services for:
We deploy AWS-certified experts to conduct thorough assessments of IAM, S3, EC2, Lambda, VPC, and all AWS native services.
We provide a thorough examination of Entra ID, RBAC, Storage Accounts, Azure SQL, App Services, and all Azure-specific configurations.
Expert assessment of IAM, Cloud Storage, Compute Engine, Kubernetes Engine, and GCP's unique security controls.
We deliver a multi-layered approach to cloud security. From your public perimeter to your deepest internal systems, our cloud pentest services find and help fix critical vulnerabilities before attackers can exploit them.
We create a simulation of an actual external attacker who will demonstrate the methods that hackers use to reach their first security breach. This service fortifies your first line of defense.
Tests Public-Facing Assets: Explore vulnerabilities through its web applications along with APIs and its external management interfaces which are susceptible to SQL injection and XSS attacks.
Assesses Exposed Infrastructure: Cloud compute instances like EC2, VMs, storage services S3, Blob Storage and container registries.
Maps Attack Vectors: Detects all entry points that attackers can exploit by showing how security breaches will occur through these weaknesses.
Assuming an initial breach has occurred, we test your internal security to reveal how far an attacker could move and what data they could access.
Identifies IAM & Privilege Risks: Finds dangerous misconfigurations in identity policies (IAM/Entra ID) and charts privilege escalation paths.
Tests Lateral Movement: Explores network segmentation, trust relationships, and access between internal systems to assess containment failures.
Evaluates Post-Breach Impact: The assessment determines which sensitive databases and internal applications and essential data can be accessed from the compromised system.
The proactive review process thoroughly assesses your cloud infrastructure to measure its security performance against established benchmarks. The system creates a secure operational base that meets compliance requirements while it identifies all security breaches that take place.
Compliance Benchmarking: We check compliance with CIS Benchmarks, NIST frameworks, and cloud provider best practices that apply to AWS, Azure, and GCP.
Security Protocols: Analysis of security policies together with logging and monitoring methods which include CloudTrail and Monitor and encryption configurations and backup procedures.
Assesses Architecture Security: Evaluates the security posture of serverless functions, container orchestration (Kubernetes), and Infrastructure-As-Code (IaC) templates.
Our cybersecurity experts are just a call away.
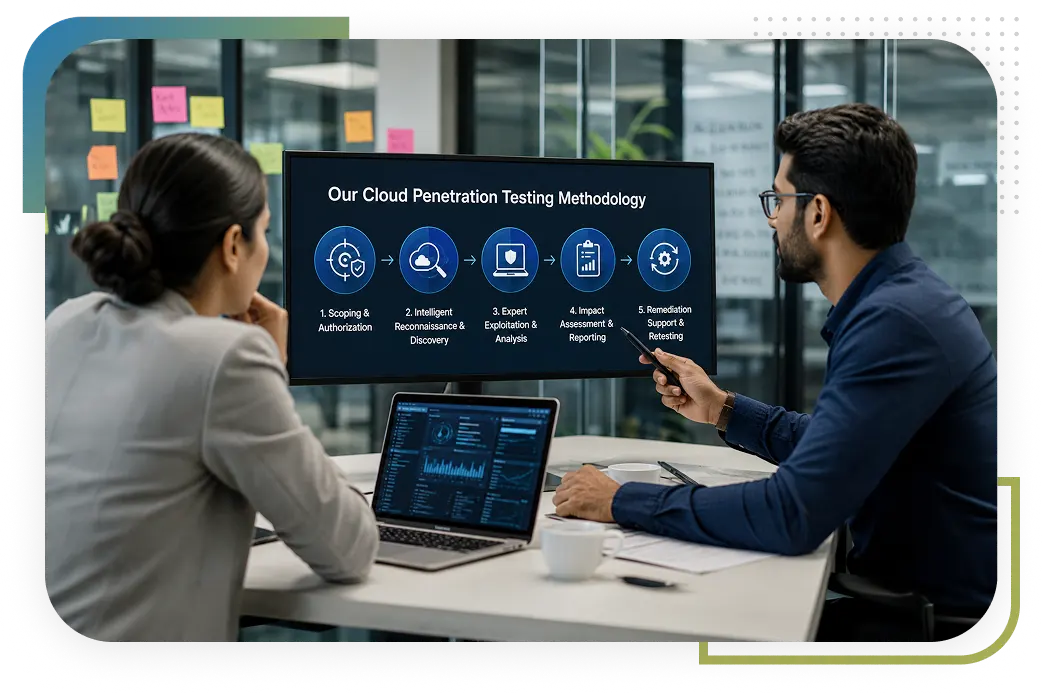
We follow precise testing guidelines that comply with all security requirements. This will prompt your cloud provider (AWS, Azure, GCP) to provide formal authorization before we conduct any testing activities.
Mapping your complete cloud footprint to identify all exposed assets, services, and potential attack vectors from both external and internal perspectives.
Our certified engineers execute manual cloud-based penetration tests which assess essential security domains that include identity and access management and data protection and network security and threats to cloud-native applications.
The process shows how each discovery affects business operations and provides a report which includes essential tasks to address security flaws in addition to presenting observed vulnerabilities.
We partner with your DevOps and security teams to validate fixes and provide retesting, ensuring vulnerabilities are fully resolved and your security posture is measurably improved.
Strengthen your cloud security and make it measurable and defensible by identifying intricate security vulnerabilities.

Permissions are given to relevant users, over-permissioned roles are identified.

No lateral movement and escalation chains.

Get summarized versions for improved business impact.

Uncover insecure settings across cloud services, storage, identity controls, and networking.

Test the effectiveness of identity management, access policies, and security monitoring.

Prioritized remediation guidance to harden configurations and reduce attack surface.
Our approach identifies security weaknesses, demonstrates their financial impact, and provides your team with direct implementation solutions.
Our engineers hold certifications in CEH Master, AZ- 500, MS 900, AZ-700, Azure Administrator, eJPT v2, and more. Our cloud experts understand how AWS, Azure, and GCP work and help their customers at every step where they face a challenge.
Beyond Key has delivered cloud penetration testing services to more than 70 organizations worldwide, helping them secure their sensitive data. We have exposed highly likely attack paths and uncovered tactical and strategic security issues and helped Fortune 500 companies.
We aim to keep your cloud environments secure and compliant across all platforms. Our professionals understand the value of GDPR, HIPAA, PCI DSS, SOC 2, and ISO 27001 requirements and adhere to these standards.
Challenge: Our client wanted to identify and remediate security vulnerabilities in its web application to prevent cyber breaches or data exploitation.
Solution: Experts at Beyond Key conducted an end-to-end penetration test to identify security challenges, assess risk factors, and provide guidance to harden the security posture of their public web app.
DOWNLOAD THE CASE STUDY →
Challenge: A SharePoint intranet connected to a public-facing website exposed the organization to potential unauthorized access and cyber threats.
Solution: Our cloud experts performed Black Box and Gray Box penetration testing to identify vulnerabilities, assess real-world attack scenarios, and help secure critical business applications.
DOWNLOAD THE CASE STUDY →
Experts at Beyond Key adhere to strict guidelines, and secure reporting procedures while defining testing scopes. This is how we protect your confidential data at every stage of cloud pen testing.
The answer to this question depends on the complexity, scope and number of cloud elements that are given for assessment. However, most cloud penetration tests take between 1-3 weeks.
We ensure that a retest is performed after the fixes are done. This helps us check whether the vulnerabilities have been resolved or not.
Yes. We provide remediation guidance, prioritize risks, and can support your team in addressing identified security issues.
Yes. We deliver cloud penetration testing services across the USA for clients from different domains. We endeavor to help enterprises secure their cloud-native environments against cyber breaches.
White-Box Cloud Penetration Testing: Our security experts are given full access to your cloud environment, including its architecture, configurations, and permissions. This helps us perform a detailed assessment and identify hidden security risks.
Black-Box Cloud Penetration Testing: Our experts test your cloud environment like an external attacker, with little or no prior information. This approach helps identify vulnerabilities that real-world attackers could exploit.
Looking for Digital Transformation?
INDIANA:

16th Floor - South Tower
Indianapolis, IN 46204
United States
ILLINOIS:
Superior St, 707
Chicago, Illinois 60654
United States
Email us for Business
Call Us
AUSTRALIA:
10 Darcy Street
Parramatta, NSW 2150
Email us for Business:
Call Us
Indore Office:
901 A, PU4, Scheme No. 54, Vijay Nagar,
Indore,
Madhya Pradesh 452010,
India
Pune Office:
Awfis, 9th Floor, Off Viman Nagar Road,
Viman Nagar,
Pune, Maharashtra 411014,
India
Hyderabad Office:
Level 6, Plot No. 38, Phase 2, HITEC City,
Hyderabad, Telangana
500081,
India
Email us for Career:
Email us for Business:
Call Us